Refresh loader

Category : Cyber Safety Services

Home > Archive for Cyber Safety Services

How Do You Modernize Fleet Tracking with a vCTO? Ultimate Guide

Virtual CTO for Logistics MSMEs: Modernizing Legacy Fleet Tracking Systems Without Disrupting Drivers

Many small logistics firms still run on old fleet tracking tools. The screens look dated. Reports arrive late. Drivers call the office to share simple updates. Owners know the system is slow, but they fear change. A virtual CTO for logistics MSMEs can help fix this without chaos on the road.

MSME stands for micro, small, and medium enterprises. These firms move goods across cities and states. They run on thin margins and tight schedules. One bad rollout can delay deliveries and upset clients. This guide shows a safer way to modernize, with drivers at the center.

Why Legacy Fleet Tracking Systems Hold Logistics MSMEs Back

Legacy fleet tracking means older GPS devices and outdated software. Some systems update vehicle location only every few minutes. Others run on servers that few people can fix. Many do not connect with billing, e-way bills, or customer apps. Data sits in silos, and teams rely on phone calls.

Many old systems were installed years ago. Devices were fitted by vendors who no longer offer support. Manuals are lost, and passwords are forgotten. Data is stored on a single office computer. As a result, one power cut can erase months of records. Owners depend on one person who knows how everything works.

These gaps carry real costs. Dispatchers cannot see true vehicle status. Customers ask for updates that staff cannot give quickly. Fuel waste and idle time go unnoticed. As a result, owners lose money in small leaks that add up each month.

Security is another concern. Old software often lacks updates and strong login rules. Vendor support may end without warning. A failure could leave you blind to your whole fleet. Therefore, waiting is also a risk.

Compliance adds pressure. Clients now ask for delivery proof, live tracking links, and clean records. E-way bill checks and audits go faster when data is digital. Firms with old systems are left behind in tenders.

Still, many owners hesitate. They worry about cost, downtime, and driver anger. Those fears are valid. Yet a careful plan can address each one. That is where a virtual CTO adds value.

What Does a Virtual CTO Do for Logistics MSMEs and Tracking?

A virtual CTO is an experienced technology leader who works part-time or on demand. You may hear the term fractional CTO too. This person sets your technology plan, picks vendors, and guides your team. You get senior advice without a full-time salary. That suits small firms that cannot afford a full-time chief technology officer.

Here is what a virtual CTO usually covers. First, they audit your current systems, devices, and data. Next, they map your needs, such as live tracking, route planning, and driver safety. They compare vendors and negotiate terms. They manage the rollout and train your people.

A virtual CTO protects you from costly mistakes. They read contracts and check data ownership. They test security and backup plans. Moreover, they keep the project tied to business goals such as on-time delivery and lower fuel cost. Technology stays a tool, not a distraction.

Trust matters as much as skill. A good virtual CTO is chosen for logistics knowledge, not just technical skill. References should be checked and past projects reviewed. Fees are agreed in advance, with a clear scope. Regular review calls are scheduled with the owner.

How to Modernize Fleet Tracking Without Disrupting Drivers

Drivers decide whether a new system works. If the app is hard to use, they will skip it. If they feel watched, they will resist. Good modernization respects their time and trust. These steps help you get it right.

Step 1: Audit and Listen First

First, begin with a full audit of devices, software, and data flows. Talk to drivers, dispatchers, and customers. Ask what slows them down today. Ask what they fear about change. Their answers shape the design of the new system.

Step 2: Set Clear Goals

Next, pick a few goals you can measure. For example, fewer late deliveries, less idle time, and faster proof of delivery are good goals. Avoid a long wish list. Clear goals keep the project focused. They help you show wins later.

Step 3: Choose Simple, Driver-Friendly Tools

Look for apps with large buttons, local language support, and low data use. Test them on basic phones and weak networks. Choose tools that work offline and sync later. In contrast, avoid heavy apps that drain battery. Simple tools win drivers over quickly.

Hardware needs a plan too. Old devices can be reused if they meet the needs of the new software. New devices are installed during normal vehicle service to avoid extra downtime. Wiring is checked by a trained technician. Spare units are kept at each depot.

Step 4: Run a Small Pilot

Test the new system with a handful of trusted drivers and vehicles. Run it side by side with the old system for a few weeks. Compare data for accuracy. Collect feedback every week. Fix problems before you go wider.

Choose pilot routes that are typical, not easy. Include one long haul and one city route. Weak mobile network zones should be tested too.

Step 5: Explain the Why and Train in Short Sessions

Additionally, tell drivers how the system helps them. It can prove on-time arrival, protect them from false claims, and speed up payments. Share how you will use location data and what you will not use it for. Moreover, keep training short and hands-on. Pair new drivers with a peer champion.

Driver concerns are real and should be heard. Location tracking may feel like spying to some crews. Rules for data use should be written in simple words. Personal trips and rest breaks must be respected. Trust is earned when promises are kept.

Step 6: Roll Out in Phases

Move route by route or depot by depot. Keep the old system as a backup until the new one proves stable. Track issues in a simple log. Celebrate small wins with your team. Finally, retire the old system only after a clean handover.

Support must be ready during the first week. A helpline is staffed by trained people, and quick fixes are documented. Common questions are turned into a short guide in the local language.

Measuring Success and Managing Risk

Track results from day one. Watch on-time delivery rate, fuel use, idle time, and customer complaints. Watch driver app usage and support calls too. Share results with the team each month. People stay motivated when they see progress.

Small wins should be shared early. A weekly note with three numbers is enough. Charts are posted at the depot for everyone to see.

Meanwhile, guard your data. Choose vendors that allow data export and clear ownership. Set access rules for staff. Back up records often. Ask about uptime promises and support hours.

Insurance and compliance need attention. Tracking data is sometimes requested by insurers and clients. Records should be stored safely and shared only with the right people. Vendor lock-in is worth avoiding, so contracts should include data export rights.

Similarly, plan for cost with care. Compare device costs, software fees, and training time. Include support and upgrade fees in your math. A virtual CTO can build a simple business case. You can phase spending to match your cash flow.

Finally, plan for the next step. Modern platforms can add route optimization, temperature sensors, and driver safety alerts. They can link to billing and customer portals. You do not need everything on day one. Build a base you can grow.

Final Thoughts: Modernize With Drivers, Not Around Them

Legacy fleet tracking does not have to hold your business back. A virtual CTO for logistics MSMEs gives you expert guidance at a fair cost. The safest path starts with listening, moves through a pilot, and grows in phases. Drivers stay at the center of every choice.

Start with a simple audit of your current tools this month. List the top three pain points. Talk to your drivers before you talk to vendors. Small, thoughtful steps lead to a smooth upgrade.
How Do You Modernize Fleet Tracking with a vCTO

Frequently Asked Questions

What is a virtual CTO for logistics MSMEs?

It is a part-time or on-demand technology leader for small logistics firms. They plan your tech, choose vendors, and guide rollouts without a full-time salary.

How do I modernize legacy fleet tracking systems safely?

Audit your system, set clear goals, and run a pilot with a few drivers. Keep the old system as a backup during rollout. Move in phases.

How can I get drivers to accept a new fleet tracking app?

Involve them early, keep the app simple, and explain the benefits. Offer short training and peer champions. Be clear about data use.

Is a virtual CTO cheaper than a full-time CTO?

Usually, yes. You pay for the time you need. Small firms get senior guidance at a lower cost.

What features should modern fleet tracking software have?

Look for live GPS tracking, offline support, route planning, alerts, and reports. Check billing links and data export too.

Also Read:

How Does vCTO Governance Fix IT Vendor Confusion? Ultimate Guide

How Do You Get Started With Smart Payments? Ultimate Guide
 

How Do UPI MDR Charges Impact Businesses in 2026? Ultimate Guide

UPI MDR 2026: What the New Merchant Charges Mean for Indian Businesses

UPI has changed how India pays for things. It is fast, simple, and mostly free for customers. However, a new update called UPI MDR 2026 is bringing changes for merchants.

MDR stands for Merchant Discount Rate. It is a small fee charged on transactions. For years, UPI payments carried no MDR for most merchants. That is now shifting for certain categories of businesses.

This article breaks down what UPI MDR 2026 means. You will learn who pays, how much, and what steps your business should take next.

What Is UPI MDR and Why Is It Changing

MDR is a fee that a merchant pays to accept a digital payment. Card payments have always included this fee. UPI, however, was mostly fee-free to encourage adoption across India.

That approach helped UPI become the most used payment method in the country. Millions of small businesses adopted it because it cost nothing to accept. As a result, digital payments grew rapidly, even in small towns and rural areas.

Now that UPI has matured, regulators and payment providers are introducing MDR for specific transaction types. This helps cover infrastructure costs and supports continued innovation in the payments ecosystem.

It is important to note that these charges typically apply to larger merchants or specific payment instruments, not everyday personal transactions. Therefore, most individual users will not notice any difference in their daily UPI use.

Who Will Be Affected by UPI MDR 2026

Not every business feels the same impact. Large enterprises processing high transaction volumes are more likely to see new charges applied. Similarly, certain prepaid instruments and wallet-linked UPI payments may carry a small fee.

Small merchants and individual sellers often remain exempt, especially those below certain transaction thresholds. This protects small shop owners and street vendors who rely heavily on UPI for daily sales.

E-commerce businesses and D2C brands should pay closer attention. Higher transaction volumes mean even small fees can add up over a month. For example, a business processing thousands of transactions may see a noticeable shift in payment processing costs.

SaaS companies and subscription-based businesses should also review their payment setup. Recurring UPI payments at scale may fall under new charge categories depending on the payment provider’s policies.

Additionally, fintech companies offering UPI as part of their platform must update their fee structures and communicate clearly with their own merchant customers. Transparency here builds trust during a period of change.

How to Prepare Your Business for the New Charges : UPI

Preparation starts with understanding your own transaction data. Review how many UPI payments your business processes monthly and which categories they fall under.

Next, speak with your payment gateway provider. Ask directly whether your account falls under the new MDR structure and what the exact rate will be. Providers should be able to give clear, written answers.

It also helps to review your pricing strategy. If new charges apply, some businesses choose to absorb the cost, while others adjust pricing slightly to cover it. Consider your customer base before making this decision, since price sensitivity varies across industries.

Furthermore, diversify your payment options where possible. Offering multiple payment methods reduces dependency on a single channel and protects your margins if fees change again in the future.

Finally, keep your accounting team informed. Payment processing fees affect your profit margins, so accurate tracking is essential for financial planning and tax reporting.

What This Means for the Future of Digital Payments in India: UPI

UPI MDR 2026 signals a shift toward a more sustainable payments ecosystem. Free services cannot last forever, especially as transaction volumes reach massive scale.

This change may also open the door to better services. Payment providers earning revenue through MDR can reinvest in fraud protection, faster settlements, and improved customer support.

For businesses, this is also a moment to evaluate technology partners. Working with a reliable payment provider becomes even more important when fees and rules evolve. Choosing wisely now can prevent costly surprises later.

Consequently, businesses that stay informed and proactive will handle this transition more smoothly than those who wait until the changes take effect. Being prepared is always cheaper than reacting under pressure.

Retail businesses, in particular, should watch how MDR impacts point-of-sale UPI transactions, since in-store volumes can be significant. Meanwhile, professional services firms billing clients through UPI links should also review their invoicing tools for updated fee disclosures.

Common Questions Business Owners Are Asking

Many business owners want to know exactly how much they will pay. The honest answer is that rates vary depending on transaction type, merchant category, and payment provider. There is no single flat number that applies to everyone.

Some worry that customers will move away from UPI toward other payment methods. This is unlikely for most industries, since UPI remains fast and convenient. Customers rarely notice merchant-side fees unless prices visibly increase.

Others ask whether MDR charges are negotiable. In some cases, payment providers offer tiered pricing based on volume. Larger businesses processing high transaction counts may qualify for better rates. It is always worth asking directly instead of assuming a fixed cost.

There is also confusion about whether MDR applies retroactively. Typically, new charges apply only from the effective date onward, not to past transactions. However, always confirm this with your specific provider to avoid billing surprises.

Business owners in the marketing and operations space should also loop in their finance managers early. Cross-team communication ensures nobody is caught off guard when new charges appear on monthly statements.

Steps IT and Finance Teams Should Take Together for UPI

Technology and finance teams often work separately, but UPI MDR 2026 requires coordination. IT managers should confirm that payment integrations are updated to reflect new fee structures accurately.

Finance managers, meanwhile, should update budgeting models to account for potential new costs. Even a small percentage fee can affect quarterly projections when transaction volumes are high.

Operations managers can help by reviewing which departments or product lines generate the most UPI transactions. This data helps prioritize where cost management efforts should focus first.

Digital transformation leaders should also view this as an opportunity. Instead of only reacting to fee changes, businesses can use this moment to modernize their entire payment stack. Upgrading systems now can prevent larger disruptions during future regulatory updates.

Ultimately, cross-functional planning turns a potentially stressful change into a manageable business adjustment. Teams that communicate early tend to handle transitions far more smoothly.

Conclusion

UPI MDR 2026 marks an important shift in how digital payments work in India. While most everyday users will see little change, businesses processing high transaction volumes need to prepare carefully.

Understanding who is affected, reviewing your payment provider’s policies, and adjusting your strategy early will help your business adapt smoothly. Digital payments remain one of the most efficient ways to do business in India, and staying informed keeps you ahead of the curve.

How Do UPI MDR Charges Impact Businesses in 2026


Frequently Asked Questions

  1. What is UPI MDR? UPI MDR, or Merchant Discount Rate, is a small fee charged to merchants for accepting UPI payments under certain conditions.
  2. Will customers pay more because of UPI MDR 2026? Generally, MDR is charged to merchants, not customers, though some businesses may adjust pricing to cover the cost.
  3. Are small businesses exempt from UPI MDR 2026? Many small merchants below certain transaction thresholds remain exempt, though rules can vary by provider.
  4. How can I check if my business is affected? Contact your payment gateway or bank directly to confirm your transaction category and applicable charges.
  5. Does UPI MDR 2026 affect personal UPI transfers? No, personal peer-to-peer UPI transfers are generally not affected by these merchant-focused charges.

Also Read:

How Do You Get Started With Smart Payments? Ultimate Guide
What Is the vCTO Guide to Automated Quality Gates? Ultimate Guide

When Your Offshore Team Delivers Bad Code: How a vCTO Sets Up Automated CI/CD Code Quality Gates

Introduction

You hired an offshore team to move faster and save money. Instead, bugs keep slipping into production. Releases feel risky. Your in-house developers spend more time fixing code than building features. This situation is more common than most founders admit. The good news is that it is fixable, often without replacing your entire team. A virtual CTO, or vCTO, can step in and build automated CI/CD code quality gates that catch problems before they reach customers. This guide explains how that process works, why it matters for founders and managing directors, and what steps a vCTO typically takes to turn a struggling offshore relationship into a reliable one. You will also learn what to realistically expect during the transition, so you can set the right timeline with your team.

Why Offshore Code Quality Problems Happen

Offshore teams are not inherently worse than in-house developers. However, several factors commonly lead to quality issues. First, communication gaps create misunderstandings about requirements. A feature built based on an unclear specification often needs rework, and rework increases the chance of introducing bugs.

Second, many offshore engagements lack strong technical oversight. If nobody senior reviews code architecture regularly, small shortcuts accumulate into larger problems. Individually, each shortcut may seem harmless. Over time, though, they create fragile systems that break unpredictably.

Third, time zone differences slow down feedback loops. A code review comment sent at the end of your day may not get addressed until the next day, and by then, the developer has often moved on to other tasks. This delay makes catching mistakes early much harder.

Finally, without automated checks, quality depends entirely on individual developer discipline. Some developers write clean, tested code consistently. Others do not, especially under deadline pressure. Without a system that enforces standards automatically, quality becomes inconsistent across the team.

Contract structure can also play a role. Teams paid strictly by the hour or by feature count sometimes prioritize speed of delivery over long-term maintainability. This is not a character flaw. It is simply a natural response to how incentives are set up. A vCTO often addresses this indirectly, by making quality an automatic requirement rather than something that depends on incentives alone.

The Founder’s Dilemma: Trust vs Control

As a founder or managing director, you likely did not hire an offshore team to micromanage every commit. You wanted to focus on strategy, growth, and customers. However, when bad code repeatedly reaches production, you are forced back into the weeds, reviewing pull requests yourself or escalating every bug.

This creates a difficult tension. Too much oversight slows the team down and defeats the purpose of outsourcing. Too little oversight lets quality problems compound. Many founders swing between these extremes, alternating between hands-off trust and sudden, frustrated intervention after a bad release.

A vCTO resolves this tension differently. Instead of relying on personal oversight, a vCTO builds automated systems that enforce quality standards consistently, regardless of who writes the code or where they are located. This shifts the burden from human vigilance to automated infrastructure, which does not get tired, distracted, or rushed.

This approach also protects the relationship itself. When problems are caught by an impartial system rather than a frustrated founder, conversations become less personal and more productive. Developers receive clear, specific feedback from the pipeline rather than vague complaints after the fact. Over time, this reduces tension on both sides and keeps the working relationship focused on solving problems together.

How a vCTO Sets Up Automated CI/CD Code Quality Gates

The process typically starts with an audit of your current pipeline. A vCTO reviews how code moves from a developer’s machine to production. This includes checking whether tests run automatically, whether code style is enforced, and whether any manual steps create bottlenecks or risk.

Next, the vCTO establishes automated testing as a non-negotiable gate. Every code change must pass a defined suite of tests before merging. If tests fail, the code simply cannot proceed. This single step eliminates a large share of bugs that previously reached production through rushed or incomplete reviews.

Static code analysis tools come next. These tools automatically scan code for common issues, such as security vulnerabilities, unused variables, or overly complex functions. Because this happens automatically, it does not depend on a reviewer noticing the problem manually.

The vCTO also typically sets minimum code coverage thresholds. If new code lacks sufficient test coverage, the pipeline blocks the merge. This encourages developers to write tests as part of their normal workflow, rather than treating testing as optional extra work.

Peer review requirements are formalized as well. Rather than relying on informal habits, the pipeline enforces that a second engineer must approve any change before it merges. Combined with automated checks, this creates multiple layers of protection against low-quality code.

Finally, the vCTO sets up deployment gates that require all previous checks to pass before code reaches staging or production. This ensures that even if something is missed earlier, the final gate provides one more opportunity to catch problems before customers are affected.

Many vCTOs also add automated rollback procedures at this stage. If a deployment causes errors after release, the system can revert to the previous stable version quickly, often within minutes. This safety net matters greatly for founders, since it limits the damage of any issue that slips through earlier checks.

What Founders Should Expect vCTO does During This Process

Implementing these changes takes time, typically a few weeks depending on your existing setup. During this period, expect an initial slowdown as the team adjusts to new requirements. This is normal and temporary. Teams unfamiliar with strict quality gates often need time to build habits like writing tests alongside new features.

You should also expect more visibility into your development process. A good vCTO sets up dashboards showing test pass rates, code coverage trends, and deployment frequency. This gives founders and managing directors a clear, non-technical way to track improvement over time, without needing to read code personally.

Additionally, expect some initial resistance from the offshore team, especially if they were previously working without strict oversight. This is manageable with clear communication about why the changes matter. Most developers actually prefer working within clear standards once they experience fewer late-night bug fixes and emergency rollbacks.

Over time, the relationship between your business and the offshore team typically improves. With automated gates in place, trust shifts from being based on hope to being based on evidence. Releases become more predictable, and the constant firefighting that often damages offshore partnerships fades considerably.

Founders often notice a secondary benefit as well: faster onboarding for new developers. When quality standards live inside the pipeline rather than inside individual habits, a new engineer joining the offshore team can get up to speed quickly. The system itself teaches expectations, instead of relying on tribal knowledge that takes months to absorb informally.

What Is the vCTO Guide to Automated Quality Gates

Conclusion

Bad code from an offshore team is rarely a permanent problem. It is usually a symptom of missing structure, not a reflection of your developers’ abilities. By introducing automated CI/CD code quality gates, a vCTO replaces inconsistent manual oversight with reliable, repeatable standards. Testing, static analysis, coverage thresholds, and peer review all work together to catch problems before they reach your customers. If your offshore team keeps delivering shaky code, the solution may not be replacing them. It may be building the right guardrails around their work. Build your authority with Ouriken Consulting and bring lasting stability to your development process.

Frequently Asked Questions

1. What does a vCTO do differently than an in-house CTO?

A vCTO provides senior technical leadership on a flexible basis, often focusing on systems, processes, and oversight rather than daily management tasks.

2. How long does it take to set up CI/CD code quality gates?

Most implementations take a few weeks, depending on the current state of your pipeline and the size of your codebase.

3. Will code quality gates slow down my offshore team?

There is often a short adjustment period, but most teams become faster over time as fewer bugs require emergency fixes later.

4. Can automated quality gates fully replace code reviews?

No. Automated checks catch many issues, but human peer review remains important for judgment, architecture, and context that tools cannot fully evaluate.

5. Is hiring a vCTO cheaper than hiring a full-time CTO?

Typically, yes. A vCTO offers senior expertise on a part-time or project basis, making it a cost-effective option for growing companies.

Also Read:

How Do FinTech Apps Handle 50k Active Users? Ultimate Guide

How Do You Know If You Need a Virtual CTO? Complete Guide

The Ultimate Checklist: Is Your Business Ready for a Virtual CTO?

Introduction

Growing a business without strong technical leadership is risky. Many founders delay hiring a full-time CTO because of cost. Meanwhile, technology decisions pile up without expert guidance.

A Virtual CTO fills this gap. This role offers experienced leadership on a flexible, part-time basis. Companies get strategic direction without the cost of a full executive salary.

This checklist helps you decide if a Virtual CTO fits your business right now. You will learn the key signs, common mistakes, and questions to ask before making this decision.

By working through each section, you will gain a clear, honest view of your current technology gaps. That clarity makes the decision to hire, or wait, much easier to make with confidence.

Signs Your Business Needs a Virtual CTO

The first sign is a lack of technical direction. If your team builds products without a clear technology road map, problems multiply quickly. A Virtual CTO brings structure to this chaos.

Another sign is founder overload. Many non-technical founders try to manage engineering decisions themselves. This slows growth and increases the risk of costly mistakes.

Rapid growth also creates pressure. As customer numbers rise, systems need to scale smoothly. Without expert oversight, technical debt builds up fast and becomes expensive to fix later.

Finally, watch for repeated project delays. If development timelines keep slipping, this often points to weak technical leadership rather than a weak team.

Security blind spots are another red flag. Without a leader focused on risk, vulnerabilities often go unnoticed until a breach happens. By then, the cost of fixing the problem is much higher.

Vendor sprawl can also signal the need for oversight. Businesses that accumulate disconnected tools and platforms over time usually lack someone responsible for a coherent technology strategy.

Difficulty attracting technical talent is another common indicator. Skilled engineers want strong leadership above them. Without it, hiring becomes harder and turnover often rises within the technical team.

Watch also for a growing gap between business goals and what the technology can actually support. When sales promises outpace product capability, a Virtual CTO can help realign expectations quickly.

Recurring downtime or performance issues are worth flagging too. If customers regularly experience outages or slow load times, this usually points to deeper architectural problems that need expert attention.

Finally, pay attention to how technology decisions get made today. If choices happen reactively, without any long-term plan behind them, that pattern alone justifies bringing in dedicated leadership soon.

Track how much time leadership spends firefighting technical issues versus planning ahead. A high ratio of reactive work is one of the clearest signals that dedicated leadership is overdue.

Key Questions to Ask Before Hiring a Virtual CTO

Start by asking what specific problems you need solved. Do you need help with architecture, security, hiring, or vendor selection? Clear answers help you find the right fit.

Next, consider your budget realistically. A Virtual CTO costs far less than a full-time executive. However, you still need a clear budget range before starting conversations.

Ask how involved you want this person to be. Some businesses need weekly strategic input. Others need daily hands-on guidance during a major product launch.

Finally, ask about industry experience. A Virtual CTO with relevant background understands your challenges faster. This experience often shortens the time needed to see real results.

Ask about communication style as well. Some Virtual CTOs prefer detailed written reports, while others favor regular calls. Choosing a style that fits your team improves collaboration from the very first week.

Request references from past clients too. Speaking with businesses of similar size and industry gives you honest insight into how a candidate performs under real pressure.

Clarify decision-making authority upfront. Some businesses want a Virtual CTO to advise only, while others want them to make final technical calls. Both models work, but the expectation needs to be clear from the start.

Discuss availability during emergencies as well. Systems fail at inconvenient times. Knowing how quickly your Virtual CTO can respond during a crisis helps you plan for worst-case scenarios calmly.

What a Virtual CTO Actually Does

A Virtual CTO builds and manages your technology strategy. This includes setting priorities, choosing tools, and aligning tech decisions with business goals.

They also mentor internal teams. Many startups have talented developers who lack senior guidance. A Virtual CTO provides that missing leadership layer.

Risk management is another core responsibility. This includes security reviews, data protection planning, and vendor evaluation. These tasks often get ignored without dedicated oversight.

Additionally, a Virtual CTO supports investor conversations. Many investors want confidence in your technical foundation. Strong leadership here can directly influence funding outcomes.

Vendor and contract negotiations also fall under this role. A Virtual CTO can evaluate software licenses, hosting agreements, and development contracts to make sure the business gets fair value.

Hiring support rounds out the role too. Many Virtual CTOs help interview and onboard technical staff, ensuring new hires match both the skill level and culture the business actually needs.

Documentation and process building matter as well. A good Virtual CTO creates clear standards for code reviews, deployments, and security practices. These processes outlast any single project and protect the business long term.

They also serve as a translator between technical and non-technical stakeholders. This skill alone often prevents miscommunication that would otherwise derail product timelines or budget approvals.

How to Evaluate Virtual CTO Readiness in Your Business

Start with an honest audit of your current technology stack. List outdated systems, security gaps, and scaling limitations. This audit reveals how urgent the need really is.

Review your team’s current skill gaps next. If nobody owns architecture decisions or long-term planning, this is a strong signal that outside leadership would help.

Consider your growth trajectory as well. Businesses planning to scale quickly benefit most from early Virtual CTO involvement. Waiting too long often means fixing bigger, costlier problems later.

Finally, weigh cost against risk. A Virtual CTO’s fee is usually smaller than the cost of a single major technical failure. This makes the investment easier to justify for most growing businesses.

Talk to your team as part of this evaluation. Developers and product managers often see gaps that founders miss. Their input gives a more complete picture of true readiness.

Set a trial period if you remain unsure. Many Virtual CTOs offer a short initial engagement. This lets both sides confirm the fit before committing to a longer-term arrangement.

Map out a rough twelve-month technology road map before you begin. Even a simple outline helps a new Virtual CTO understand your priorities and start contributing value from the very first meeting.

Revisit your readiness assessment every quarter. Business needs change quickly, and a checklist completed six months ago may no longer reflect your company’s current technical reality.

The ultimate checklist: Is your business ready for a Virtual CTO?

Conclusion

A Virtual CTO offers experienced leadership without the cost of a full-time hire. This checklist helps you spot the signs, ask the right questions, and evaluate true readiness.

If your business faces technical delays, founder overload, or unclear strategy, the time to act is now. Waiting longer usually increases both cost and risk.

Businesses that bring in the right guidance early often scale faster and avoid painful, expensive rebuilds. The sooner the gap gets addressed, the smaller the eventual fix tends to be.

Technology decisions made today shape how easily your business grows tomorrow. A short conversation now can save months of rework later, especially as customer demand and system complexity increase.

Ready to strengthen your technology leadership? Build your authority with ouriken Consulting and gain the strategic guidance your business needs to scale with confidence.

Frequently Asked Questions

1. What does a Virtual CTO do differently from a full-time CTO?

A Virtual CTO provides the same strategic leadership on a flexible, part-time basis. This makes expert guidance affordable for businesses not ready for a full-time hire.

2. How much does a Virtual CTO typically cost?

Costs vary based on hours and scope, but a Virtual CTO usually costs significantly less than a full-time executive salary and benefits package.

3. When should a startup hire a Virtual CTO?

Startups should consider a Virtual CTO when facing unclear technology strategy, founder overload, or rapid growth that outpaces current technical leadership.

4. Can a Virtual CTO help with investor meetings?

Yes. A Virtual CTO can strengthen technical credibility during investor conversations, which often improves confidence in the company’s overall readiness.

5. Is a Virtual CTO suitable for non-technical founders?

Absolutely. Non-technical founders benefit greatly from a Virtual CTO, since this role translates technical decisions into clear business outcomes.

Also Read:

How Should Growing D2C Brands Handle Payments: Complete Guide

How Does a Virtual CTO Guide Tech Planning? Complete Guide

The Zero Trust Shift: Securing Hybrid Work with ZTNA

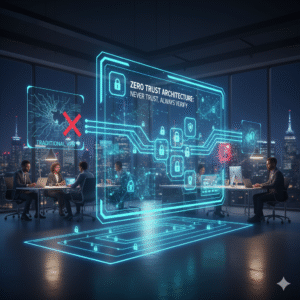
The old security walls are gone. Hybrid work is the norm today. Relying on the old “castle-and-moat” idea is risky. This old plan trusted all inside the work net. Consequently, Zero Trust Architecture (ZTA) is the key to safe work. Zero Trust uses one rule: never trust. Always verify.

All users, devices and data must be checked. This is true even for access inside the network. This constant check is vital.

New Zero Trust fixes are part of the net. They use smart tools like AI. They use flexible access rules. Thus, these tools give better security. Workers are everywhere now. For this reason, a strong Zero Trust plan is a must for all firms. Moreover, this plan knows threats are everywhere. Therefore, the net is never trusted by default. This change helps keep the whole system safe.

Image Of The Zero Trust Shift: Securing Hybrid Work with ZTNA

Beyond The Basics: The Evolution of ZTA Pillars

The first Zero Trust design only focused on two things. First, it focused on strong Identity and Access Management (IAM). Second, it focused on dividing the net. However, threats are much smarter now. Therefore, the whole design has changed. Now it includes more detail. Also, it includes smarter access checks across all digital tools. Thus, these new improvements are making security stronger. Also, they are making the process clearer for the workers who use the system.


Context-Aware Access and Evaluation

Access checks cannot stay static. They cannot only depend on a name and a code. Instead, access decisions are always changing. They change based on many factors. Therefore, new Zero Trust systems check many different things. They check these things all the time. They check for every access request. This non-stop check is great.

For example, the system checks these key factors:

  • User Identity and Role: Who is the person trying to log in? What can this person do based on their job?
  • Device Posture: Is the device following all company rules? Is the system fully up-to-date? Does the device have the right virus scan running? For this reason, if a device’s score drops, the system cuts off access fast. Or, it lowers the access level right away.
  • Location and Geolocation: Where is the access request starting from? Is this a strange place for this worker to be?
  • Time of Day: Is the worker trying to look at secret data late at night? For instance, is it at 3 AM?

This continuous check means the system never just gives trust easily. Access can quickly change. Also, the system can stop access right in the middle of a session. This happens if the risk goes up. This action prevents a hacker from moving inside the net. Therefore, Zero Trust gives great control.


The Rise Of AI And Automation

Artificial intelligence (AI) is the main power source for the next step in Zero Trust. AI and machine learning look at huge logs of data. They do this in real time by looking for strange things. They flag risky actions that people would miss. This speed is vital now.

New AI improvements give great help. For example, AI-driven fixes include:

  • Automated Data Classification: AI automatically reads and sorts data. It gives the data labels like “Secret.” This task is crucial. This ensures that the rules for Data Loss Prevention (DLP) work right. This is true no matter where the data is kept. This helps protect private customer details.
  • Behavioral Analytics: The system learns what is normal for a user. Consequently, if a worker suddenly uses an app they never touch, the AI sees it. Or, if the worker starts getting too much data, the AI detects the odd change. Then, the system forces a re-check. Or, it blocks the action. This step helps a lot. It also stops bad behavior.

The system uses Threat Detection and Response (XDR). XDR combines security facts. It gathers data from emails and computers. It gives a full picture of any threat. Thus, the system can quickly block bad computers or users. Truly, Zero Trust gets its power from these tools.


From VPN to ZTNA: Securing The Hybrid Workforce

The biggest change in the Zero Trust setup is the move from old VPNs. Now, everyone uses Zero Trust Network Access (ZTNA). This move is necessary. It secures all remote work teams.

VPNs had a major fault. They gave a user access to the whole net once checked. This was a single point of failure. Conversely, ZTNA replaces this old way. It uses true least-privileged access. Therefore, a remote worker only makes a small, safe link. This link goes only to the one app the worker needs. It does not connect to the whole net.

This change has many pluses. The attack area shrinks greatly. Thus, it makes it hard for a hacker to find a way in. Also, the risk of harm is low if a computer is hacked. This cuts the “blast radius” of any break-in. ZTNA also runs quietly. It is fast and better for the user. It avoids the slow-down issues that were common with old VPNs. Thus, choosing ZTNA is a main step toward full Zero Trust.


ZTNA Versus VPN Comparison

Feature Old VPN Model Zero Trust Network Access (ZTNA)
Trust Model Implicit Trust (Trusts all once door opens) Never Trust, Always Verify (Checks every action)
Access Granularity Grants network access (You get the whole floor) Grants application access (You get one desk)
Attack Surface High (Exposes the net to hackers) Low (Apps stay hidden from hackers)
Lateral Movement Easy (Hacker moves freely) Blocked (Access is limited to one app)

ZTNA simplifies security a lot. You do not need to check complex firewall rules for every user. Instead, the rule is based on the user’s name. This rule follows the user. Thus, the security stays the same everywhere. Consequently, ZTNA fixes the main problem of securing workers who move often.


Key components for a robust zero trust workspace

Building a full ZTA needs many layers of defense. You must cover every part of your digital work area. These three core parts work well together. They deliver very strong workspace security.

1. Identity and Endpoint Security

A strong system for Identity and Access Management (IAM) is the most basic need. This involves forcing all users to use Multi-Factor Authentication (MFA). MFA adds a safe step after the password. It also requires using Single Sign-On (SSO). SSO centralizes the login process. Furthermore, the focus on Endpoint Security has grown. Zero Trust Architecture checks all devices deeply. It checks phones and computers. It must ensure that all devices meet strict rules before they can connect. If a worker uses their own phone, the system keeps company info separate. This is vital.


2. Micro-Segmentation and Networking

Micro-segmentation is a powerful tool. It cuts the whole net into small zones. Gaining access to any zone needs a separate, clear pass. This stops a hacker from moving around easily. If an attacker breaches one part, their harm is small. They cannot move to the finance server from the marketing server easily. They need a new key. Likewise, the network side has changed. It now views the computers in the main office as just another untrusted part. This is key. This guarantees that the rules work the same way for every link. It does not matter if a worker is at home or in the main office.


3. Data Protection and Governance

In the end, the main job of Zero Trust is to protect the info. New fixes focus on applying consistent DLP policies. These rules apply to all apps. They work for cloud apps. They work for in-office apps. This step ensures that secret info is always safe. It must be safe when it sits still. It must be safe when it moves. Also, Zero Trust creates a full record. This audit trail shows every access try. It shows every data action. This clear record is needed. It greatly improves security. Moreover, this transparency makes meeting rules much simpler. Thus, security teams can easily prove compliance.


Conclusion: Building a Secure Future

The move to Zero Trust Architecture is not a trend. It is a required security shift. The shift to hybrid work has killed the idea of a safe net border. Consequently, firms must use the “never trust, always verify” rule. This ensures that security is used everywhere. It is used on every person and device. It does not matter where they are.

This modern security plan is built on many key fixes. For instance, ZTNA replaces old VPNs. AI uses constant checks to find threats fast. Micro-segmentation stops hackers from moving around inside the net. Furthermore, focusing on the person and the device’s health makes access choices smart. Therefore, companies that use a full Zero Trust plan will gain a major plus. They will keep their data safer. They will simplify compliance and will also give their workers a safe way to work from anywhere. Truly, a strong Zero Trust plan is the best choice for future business safety.


Frequently Asked Questions

1. What does “never trust, always verify” actually mean in practice?

It means the system checks the user every time they want to do something. For example, when a user logs in, the system checks them. When they click on a new app, the system checks them again. Consequently, the system treats the whole net as a dangerous place. It trusts nothing easily.


2. How does zero trust prevent lateral movement?

Zero Trust uses micro-segmentation. This divides the net into small, secure areas. When a user gets access, they only get a small link to just one resource. Therefore, if a hacker gets that user’s access, they cannot move to other parts of the net. They are stuck in a tiny zone.


3. Is ZTNA a replacement for my VPN?

Yes, Zero Trust Network Access (ZTNA) is now taking the place of old VPNs. VPNs gave users access to the entire net. This was risky. However, ZTNA grants access only to one specific app. This is after the user and device are fully checked. This makes security much better for people working from home.


4. How does context-aware access improve security?

Context-Aware Access makes security decisions smart. It uses real-time info. For instance, it checks the device’s health. It checks the user’s location. It uses this info to guess the risk. Then, it changes the access level right away. It can deny access if the risk is too high.


5. Why is ai so important to the latest zero trust enhancements?

AI is key because it can check for threats faster than any person. It learns what is normal. It then flags strange actions fast. This allows the system to find hackers right away. Consequently, the hacker has very little time to cause harm in the workspace.


Also Read: Latest Outlook Updates: Smarter Scheduling and AI Suggestion

101 Guides to Cyber Security

Just as there are common-sense practices that everyone should follow online, particularly companies that store personal information, just like not accepting gifts from strangers. IT service organizations see some new issues emerging with online security, but the same issues also haunt consumers over and over again. There are a few recurring themes when providing assistance to workplace cybersecurity that just doesn’t go away.

And you’ll get the info about Cyber Security 101 Guides here in this article. I hope you’ll enjoy writing up and reading. Post your questions in the comment box below.

This is followed in a nutshell by online security, including what to use and what to avoid. And nearly, everything you need to learn how to set it up so that you appreciate and access the internet for the connectivity it offers. For decades, some things in the IT space have not changed, for good reason. When online, a front-line defense is necessary.

Cyber Security Basics 101: Firewalls & VPNs

If you think that firewall is dull old operating system parts, you’re wrong. The reason that they have become embedded in the IT  lexicon is that they work, they are essential, and they are now more applicable than before. Whether it’s the resident firewall required on an individual PC or a shielded network (Intranet), using a firewall remains a critical component of cybersecurity since the internet is plugged in. A Virtual Private Network (VPN) is also mandatory in order to restrict access. As a firewall removes information from your device, this defense is carried offline by a VPN. Any modern business is asking for trouble without a VPNs shield. Hacking and information loss are like car accidents – fascinatingly horrible to read about, but it will never happen to you, right? Alright, note that there are thousands and thousands of people who wake up every day with the sole purpose of illegally making money online. It mostly includes data theft for illegal benefits, ransoming data, or even accessing online banking or other protocols of payment.  You don’t have to take it as personal assault – it isn’t Cybercrooks are opportunistic and you’re the target for today when you turn up on their radar without the basics in place. Do not believe that you are too small to be heard for a moment. Sadly, statistics show that is it indeed small and medium-sized enterprises that suffer the burnt of hacks.

Relates Post: Types of Hackers & current scenario among the types of hackers

 Cyber Security: Threats

In short, there are various forms of digital malice. Business connectivity has become constant since the baseline – which business is not always online? – it’s making you appreciate what’s out there.

Viruses

We can not expect to be cured of this dimension of cyber life just like a common cold. A virus s malicious software that affects the output of your machine, corrupting the operating system and records. They may be present without being involved, but they are usually a crippling pest again just like the flu virus.

Malware

Malware, the terms are often used interchangeably, often indistinguishable from a virus. More commonly, malware may not be corrupt systems and delete data to build your own personal nightmare, but may also contain spyware (such as key-logger apps.)

Ransomware

Ransomware. A step up in cheek and worthy of its own name, ransomware is malware that treats your data as delicately as you would, just to impenetrably lock it up and demand payment for its release! Ransomware attacks are often successful, as the prospect of losing or publicly releasing consumer or other personal data is grim for many businesses. When ransomware is at hand, it is best to call in experts who can assist with cybersecurity, while defining and enacting all possibilities and possible rescues.

Bots

A favorite of those launching a distributed denial of service (DDoS) attack, a bot (or “internet robot”) is a scheduled activity executing an application. They may also take full control of a PC, mostly responsible for removing mail addresses or financial information.

Trojans

These are still hidden malware fragments that come disguised as legitimate inputs or deals, but then open a door for further operation on a computer or network. They usually steal and keep the door open for further malicious fiddling.

Worms

Worms are still around, rigger than ever before. Worms are more proactive than a blunt virus as they are typically able to travel across networks without the need for human activity and are constantly replicating themselves.

Spam

Now, sadly, spam has continued, taken over your post box from where junk mail left off. Spam mail is often the preferred way to get any of the above horrors through the firewall, more than just an irritating annoyance. Apart from spambots posting on social media and infiltrating your feeds, spam is also a big phishing tool, whereby a crook may seek to get sensitive details from you under the pretext of some fake need, connection, or enticing deal.

spam

Cyber Safe Being and Staying

It is not difficult to take cyber security101 seriously and provides both comfort and trust when conducting digital affairs that you are secure. Reinforce passwords across all clients as a first step to secure online. Use a password maintainer that produces user and secure passwords ideally. Implement solutions for firewall, VPN and antivirus, all of which should be in operation against the backdrop of a comprehensive backup plan.

Related Post: Do’s and Dont’s of Cyber Safety Measures!

In the Ouriken Cybersafety services area, there are many things to consider and, sadly, even the best solutions will fail unless they are extremely detailed. To ensure that you are legally and fully covered for a safe cyber life, we can help ensure the integrity of your business and the sanctity of your data with online security.

Ouriken is a standalone web design and digital agency. We design and implements powerful solutions for small and medium businesses in technology, business, and operations.

[contact-form][contact-field label=”Name” type=”name” required=”true” /][contact-field label=”Email” type=”email” required=”true” /][contact-field label=”Website” type=”url” /][contact-field label=”Message” type=”textarea” /][/contact-form]

Things to Consider for Successful Cloud Migration Testing

If you have been following us, you will know that we discussed the methods which can be used in the cloud migration process itself. But most of the tines it may happen that the process of execution according to us happened correctly and efficiently, whereas, unless we test it thoroughly we cannot just assume that its concrete and it needs constant attention and maintenance to run smoothly. That is why just as we do software testing, we have to do the cloud migration testing. And in this blog, we’re going to address the testing considerations for cloud migration.

A comprehensive testing plan is crucial for the migration’s success, once you have decided to move your business to the cloud. The cloud migration process will help you to ensure that you do not face server breakdown issues, database glitches and other errors that can impede a successful cloud migration.

Focus for Cloud Migration Success

The main focus of cloud migration testing is on the various validations required to ensure its success.

Related Post: 3 Best Cloud Migration strategies You Must Know About

Functional Testing

The production-readiness of the migrated applications is tested in functional validation. For ts various aspects a detailed analysis is performed and checked for SLA compliance. Perform end-to-end validation of the applications’ functions to ensure the success of your migration

  • Checking if the desired output is generating for a valid and required input.
  • Checking if the service integrations with other applications are complete.
  • Checking if the object references are working as expected.
  • Checking if the cross-platform compatibility is ensured.

Integration Testing

To ensure your applications are integrated seamlessly with third-party applications and that communication between them is happening without and issues is an integral part of migration testing. Strikeout the dependencies between applications, and various SLAs that each application comes with. The migration process tends to become more complicated if you are migrating one or more applications. Just consider these following validations to simplify the process.

  • For integration testing, what interfaces and systems should be covered?
  • For validation and integration testing, what are the resources needed?
  • To develop and execute tests with third-party applications, what plan is in place?
  • How will the identification of coordination problems in the cloud environment?

Many Cloud consulting service providers also provide integration validation as an add-on to their services, which help ensure error-free integration testing.

integration testing, performance testing, security testing, functional testing

Security Testing

In the beginning, the biggest discouragement for organizations to move their operations to the cloud was concern over security. Backed up by several advancements in the field, cloud security now has features that can prevent even sophisticated attacks from gaining access to your data and applications. Consider the following while y perform security validation:

  • Make sure that your cloud network can be accessed only by authorized users.
  • Take preventive measures against common attacks, and ensure that the measures are working properly.
  • Validation of data security is important In rest, in use and during transit.

A few other aspects of security testing include data security, privacy testing, business process security, and application security.

Related Post: Types of Hackers & current scenario among the types of Hackers

Performance Testing

Determining the performance and response time of the applications moved to the cloud is important for determining migration success. This step will also help you in optimizing the workload across resources. These are the things you should consider while performing performance validation.

  • Checking if the application architecture is supported by the cloud.
  • As per SLAs, we have to validate response times.
  • Load testing must be performed in parallel to understand how your services perform under various load types.

Conclusion

Cloud migration is often tricky to execute despite having all that help organization can get on paper, cloud migration is often tricky to execute and can result in more problems than benefits if used misleadingly. Hence, it is important and advisable to understand why to bring a team of testing professionals on-board for a successful migration.

Ouriken is a standalone web design and digital agency. We design and implements powerful solutions for small and medium businesses in technology, business, and operations. Our cloud consulting services identify and prioritize cloud applications, optimization, cloud migration which helps your business.


[contact-form][contact-field label=”Name” type=”name” required=”true” /][contact-field label=”Email” type=”email” required=”true” /][contact-field label=”Website” type=”url” /][contact-field label=”Message” type=”textarea” /][/contact-form]

Types of Hackers & current scenario among the types of hackers

The word Hacker is not fully understood by everyone and inherently misused. A stereotypical 1980’s movie character where a hacker is an evil criminal who is conspiring against the people and government, is the visualization of people when they hear the word hacker. But in reality, a hacker is just a normal person whose computer skills are high and can manipulate and bypass computer systems to make them do the intended. Hacking is not illegal unless a hacker has malicious intent and is trying the trespass the defenses and exploit weaknesses of a system without authorized permission.

As in the 80s movies the good guys used to wear white hats and the villain used to wear the black hat, the hackers are also classified on the basis of their hats.

Unethical type of hackers – Black Hat

A computer expert who finds vulnerabilities in online security and willfully damages them for their own personal gain is a black hat hacker. They are motivated by the feelings of petty revenge by targeting the companies they don’t like and exploit their vulnerabilities to shut them down only for their frivolous reasons and also by feelings of power by infecting a computer by ransomware and then demanding money to unlock the device.

Related Post: 9 Tips to Reduce Mobile App Development

Black hats may look for any type of private information that might give them some money such as credit card numbers, passwords, Emails, and Bank Accounts data. Thus, they are called criminals with no ethics, and might even break into a computer network with an intention to destroy it rather than just stealing it.

Confused Type of hackers – Grey Hat

When compared to black hats, grey hats are less skilled or white hats are a blend of both types of hackers. Grey hats are often technology hobbyists who enjoy dabbling in minor white-collar crimes such as P2P file sharing and cracking software. They report the organization about their findings and if the organization or company does not respond or refuses to pay them, they perhaps post about the system’s weakness on online forums for the internet and the world to see.

Grey hat doesn’t usually work with malicious intent, they just search for bugs and vulnerabilities in order to get a small fee for discovering the issue. Whereas the hacker type attempt to compromise a security system without permission and that is not legal.

Ethical Hackers – White Hat

Using skills and capabilities for good and legal purposes is known as White Hat hackers. They are also known as contrasting personalities of black hat hackers. White hats are employees or freelancers or contractors who are hired to test the weak spots in security systems. This is the job which an individual get after studying cybersecurity if he is good at what he does he can also start his own company giving cyber safety services. They determine how they can improve the security measures by simulating the attacks by imitating the malicious user or black hat and help identify the vulnerabilities.

White Hat performs tests on the security systems like penetration testing and many more, they exploit a completely authorized and legal form of hacking. All this happens by taking permission from the owner first and report all the findings to the security team.

cyber security services

Current Scenario for the hackers and Conclusion

As per the experts, black hat types of hackers are the most skilled hackers and are more experienced when compared to that of most of the white type of hackers. To ensure their safety from data breaches and other security threats many former black hats have turned their life around and now work as white hats.

Related Post: What Is Business Process Management?

The requirement of ethical hacking is increasing to ensure malicious hackers do not get success in their efforts to access computer systems. Red-team, blue-team exercises and continuous penetration exercises are performed by companies to analyze and identify the weak spots, and to refine the security of their systems before the black hat types of hackers exploit them.

Ouriken is a standalone web design and digital agency. We design and implements powerful solutions for small and medium businesses in technology, business, and operations. Ouriken provides cybersecurity services and operations to effectively and efficiently detect and respond to the evolving threat landscape.

Do’s and Don’ts of Cyber Safety Measures!

Cyber Safety Measures must for all Business

The online world offers businesses the potential for reaching a broader customer base, use international suppliers and seldom even conserve on admin or supply expenses. However, the world of online business can bring the potential for scams and security risks in internet safety measures are not taken. A single successful attack could seriously damage your business and cause financial trouble for you and your clients, as well as affect your business’s status. It is important to have an update on cyber safety operation and protect your business against cybersecurity threats and make the most of the opportunities online. It’s a good idea to put an efficient cybersecurity system in place if your business accesses the internet or email to conduct business.

Here is your important checklist of do’s and don’ts when it comes to cyber safety facts and keeping your business secured from unwanted cyber attacks, hacks and human threats!

Managing administrative Password and Insist on strong passwords!

Update your operating system constantly. This is very important when new security patches come out under cyber safety information. Many computers do this automatically, just make sure you have the auto-update function switched on so you don’t miss out. Change all default passwords and look at disabling administrative access fully to evade an attacker from getting access to your computer or network. Make sure you change each password to something unique that can’t be quickly guessed, improving your digital security. Attackers own the potential to gain complete access to your system from an administrator level account.

Backing Up data

Backing up your company’s data and website may aid you as a cyber safety measure and help you recover what you’ve lost in the case of an attack. It’s crucial that you constantly back up your valuable data and information, from financial documents and business plans to client records and personal data. This will reduce the damage in the event of a breach or computer problem. Luckily, backing up your data is usually cost-effective and simple. It’s a great idea to use versatile back-up methods to further ensure the protection of your valuable files. A good back-up system typically includes daily,end-of-week, quarterly, and yearly server back-ups.

cyber safety services

Use a Virtual Private Network (VPN)

VPN’s connect your business to the network with an encrypted connection so data being shared online can’t be seen by third parties. VPN providers allow secure data connections within remote workers and your network also, which can be mainly valuable if you assign workers into the field (for deliveries or repairs, for instance).

Related Post: The Most Important Things To Consider While Redesigning Your Website

Secure your computers, laptops and mobile devices

Make sure all the devices used for work or business are secure. Don’t save important passwords on any mobile, laptop or computer device. Master how to use remote wipe capability on your phones and tablets through cyber safety services. Small portions of software identified as malware or viruses can infect your computers, laptops and mobile devices. Install security software on your company computers and devices to further prevent infection and ensure it comprises anti-virus, anti-spyware and anti-spam filters. Make sure that you set your security software to update automatically as updates may include critical security upgrades based on fresh viruses and attacks.

Educate the Staff

Educate employees on using a USB stick or portable hard drive and make them well versed with cyber safety information. An anonymous cyber threat can inadvertently transfer from a portable device from home directly into your business system. So don’t assume everyone is doing the right job, and be actively alert and across your team, their activities and all components of your business and give them enough security training. It is essential to enlighten your team on the menaces they can face online and the major role they play in keeping your business safe. Your staff needs to be aware of their computer rights and responsibilities as well as their network access usage. Be particular about the types of online methods that are acceptable when using work computers, devices, and emails.

Use spam filters

Apply spam filters to decrease the volume of spam and phishing emails that your business experiences. Spam messages are normally from a person or organization that you don’t know, and they usually include offers too real to be true. Don’t reply, try to unsubscribe or call the number given in the message. The righteous thing to do is delete them. Applying a spam filter will help lessen the risk of you or your employees opening a phishing or fraudulent email by accident. Forwarding spam emails for marketing purposes is a crime under the law coming under cyber safety operations. Notable fines apply if this crime is proven.

Related Post: Boost visits by optimizing page load time for your Website

Protect your clients

No matter the extent of your client information database, it is vital that you keep it secure. Apart from being a tremendous blow to your organization’s reputation, there may be judicial consequences for losing clients’ personal information. For various people who buy online, it is necessary to identify that their payment particulars and address are safe. It is also important for your clients to know that you will not share their details without their permission. Give a secure online environment for transactions and ensure you secure any personal information that your business may store. Communicate to your payment gateway provider about what they can do to check online payment fraud and safeguard the interest of the client through cyber safety services.

cyber safety services

Outsource overwhelm. There are plenty of companies and consultants who will happily come in, audit your business and provide solutions. Whether it is your time and money or their time and your money, this is a non-negotiable expense that will save you far more than it will cost in the long run.

Ouriken -We are at the fore of the cyber frontier, relentlessly continuing innovative solutions that give the world a secure place to experience, serve, and do business with well implemented cyber safety operations.

With decades of mission intelligence linked with the most exceptional tools possible, we preserve businesses facing the attacks of today and equip them for the warnings of tomorrow.

We are a team of experienced strategists and analysts, engineers and operators in the world’s greatest missions and we know the strategies, structures, and statistics that describe cyber enterprises and operations.