Refresh loader

Category : Data Leaks

Home > Archive for Data Leaks

How Does vCTO Governance Fix IT Vendor Confusion? Ultimate Guide

Managing 3 Different Software Vendors: Unifying Disjointed IT Agencies Under Single-Point vCTO Governance

Many growing businesses end up working with multiple IT vendors over time. One agency builds the website. Another manages cloud infrastructure. A third handles custom software development. Individually, each vendor may do good work. Together, however, they often create confusion, delays, and rising costs.

This is where single-point vCTO governance becomes valuable. A virtual CTO, or vCTO, acts as a central point of accountability across all your technology vendors. In this guide, we will explore why managing multiple software vendors is harder than it looks, and how vCTO governance solves these challenges effectively.

The Hidden Cost of Managing Multiple Software Vendors with vCTO

At first, working with several specialized vendors seems efficient. Each agency focuses on what it does best. However, coordination between vendors often falls on internal teams that lack technical depth. This creates communication gaps and slows down decision-making.

Additionally, vendors rarely share the same priorities. One agency may recommend a tool that conflicts with another vendor’s system. Without a unifying strategy, businesses end up with fragmented technology stacks. This fragmentation increases costs and creates security risks over time.

Finance managers often notice this problem first. Invoices arrive from multiple vendors with overlapping services. Meanwhile, operations managers struggle to get clear answers when something breaks, since no single vendor takes full ownership of the outcome.

Consequently, many businesses reach a breaking point. They realize that managing three or more disjointed IT agencies costs more in time and stress than it saves in specialization. This is exactly the gap that vCTO governance is designed to close.

What Is Single-Point vCTO Governance?

A vCTO is an experienced technology leader who works with your business on a fractional or contract basis. Unlike a full-time CTO, a vCTO provides strategic oversight without the cost of a permanent executive hire. This makes it accessible for startups, SMEs, and mid-sized enterprises alike.

Single-point governance means the vCTO becomes the central authority across all your software vendors. Instead of each agency reporting separately to different internal stakeholders, they report through one coordinated strategy. This eliminates conflicting priorities and creates a unified technology roadmap.

Furthermore, a vCTO evaluates each vendor’s performance against shared business goals. This includes cost efficiency, security standards, and long-term scalability. As a result, businesses gain a clear, objective view of whether their current vendor mix actually serves their needs.

This model works particularly well for businesses undergoing digital transformation. When multiple systems need to work together, having one accountable technology leader prevents costly misalignment between vendors.

How vCTO Governance Solves Vendor Management Problems

One major benefit is centralized decision-making. Instead of juggling separate conversations with three vendors, business owners get consolidated recommendations from their vCTO. This saves significant time for CEOs and operations leaders who are not technical specialists themselves.

Additionally, a vCTO standardizes communication across vendors. They set clear expectations, timelines, and reporting formats for every agency involved. This consistency reduces misunderstandings and keeps projects on track more reliably.

Security also improves under this model. A vCTO reviews each vendor’s practices against a unified security standard. This is especially important when vendors have access to sensitive customer or financial data. Without this oversight, gaps between vendors can create serious vulnerabilities.

Cost control improves too. A vCTO often identifies overlapping services between vendors that waste budget. For example, two agencies might unknowingly offer similar hosting or monitoring services. Consolidating these reduces unnecessary spend significantly.

Implementing vCTO Governance in Your Business

Start by mapping your current vendor landscape. List every software vendor, their scope of work, and their reporting relationships. This exercise alone often reveals overlaps and gaps that were previously invisible to leadership.

Next, bring in a vCTO with experience across your specific technology needs. Look for someone who has managed multi-vendor environments before, ideally within your industry. This experience helps them quickly identify risks and opportunities within your existing setup.

After onboarding, the vCTO should establish clear governance processes. This includes regular vendor review meetings, shared performance metrics, and a unified technology roadmap. These processes ensure accountability across all parties involved.

Finally, measure results over time. Track metrics like project delivery speed, incident response times, and overall IT spend. Most businesses see measurable improvements within the first few months of implementing single-point governance.

Is vCTO Governance Right for Your Business?

This model works well for businesses managing three or more active software vendors, especially when internal teams lack deep technical expertise. It also suits businesses experiencing rapid growth, where technology decisions increasingly affect broader business strategy.

However, very small businesses with a single simple software stack may not need this level of governance yet. In those cases, direct vendor management may still work fine. As complexity grows, though, revisiting this decision becomes important.

Business transformation leaders and innovation heads should evaluate this option seriously. The cost of ongoing vendor confusion often exceeds the investment required for proper governance. Early adoption can prevent larger, more expensive problems later.
How Does vCTO Governance Fix IT Vendor Confusion

Conclusion

Managing three different software vendors without a unified strategy creates unnecessary risk and cost. Single-point vCTO governance solves this by placing one accountable expert at the center of your technology decisions. This leads to better security, clearer communication, and smarter spending across your entire IT ecosystem. For growing businesses, this approach often marks a turning point toward more efficient, confident technology management.

Frequently Asked Questions

  1. What does a vCTO actually do day to day? A vCTO oversees technology strategy, manages vendor relationships, and ensures all software decisions align with business goals.
  2. How is a vCTO different from a full-time CTO? A vCTO works on a fractional or contract basis, offering executive-level expertise without the cost of a permanent hire.
  3. How many vendors justify hiring a vCTO? Businesses managing three or more active software vendors typically benefit most from single-point vCTO governance.
  4. Does vCTO governance replace my existing vendors? No, it coordinates and oversees existing vendors rather than replacing them, improving alignment and accountability.
  5. Can small businesses afford vCTO governance? Yes, the fractional model makes vCTO governance accessible for SMEs and startups without full executive budgets.

Also Read:

How Do UPI MDR Charges Impact Businesses in 2026? Ultimate Guide

How Do You Get Started With Smart Payments? Ultimate Guide
 

How to Share Google Drive Files with External Clients Safely

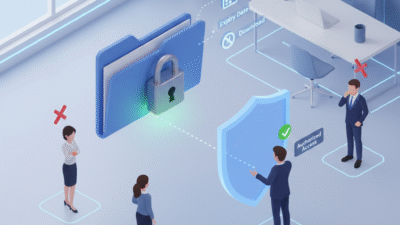
You must protect your business secrets when you work with people outside your firm today. Therefore, you should learn how to share Google Drive files with external clients safely. Truly, a single wrong click can expose your private data to the whole web. Consequently, you can secure your digital assets by using the right sharing tools for 2026.

Many people think that clicking a “Share” button is all they need to do. But, the reality is that open links can lead to big security risks for you. Always remember, a secure file system is a strong signal for any search engine. This ensures that your brand stays professional and your client data stays very private. This approach requires you to set strict rules for every document you send out. It helps you build a much more reliable business for the long term. It makes your daily digital collaboration feel much more secure and very effective.

Google Drive


Using Specific Email Access instead of Public Links

First, you must stop using the “Anyone with the link” setting for private work. Why is sending a public link so dangerous for your business? Clearly, anyone who finds that link can see your files without your permission. Therefore, you must only invite specific email addresses to view your documents in 2026.

The Benefits of Direct Email Sharing

Here are several reasons why direct sharing is a win for your safety:

  • Access Control: Only the people you invite can open the file.

  • Identity Proof: Google checks their email before they can see the data.

  • Revoke Power: You can remove a single person’s access in one second.

  • Tracking: You can see exactly who opened the file and when.

  • No Leaks: If the link is forwarded, the new person cannot see anything.

  • Professionalism: Clients feel safer knowing you take their privacy seriously.

  • Search Engine Value: Secure data handling improves your overall brand trust.

Truly, these steps solve the problem of accidental data leaks in just a few clicks. But, you must also check your sharing list every month to remove old clients. This keeps your file system clean and prevents any sudden data breaches for your firm. It creates a very high and professional standard for your daily digital security.


Setting Expiry Dates and Disabling Downloads

So, how do you ensure a client loses access once a project is finished? Truly, you do not want your old files sitting in a stranger’s folder forever. Consequently, you should use “Expiry Dates” to automatically lock your files in 2026. It acts as a direct fix for long-term security risks.

Advanced Sharing Settings for Extra Safety

Here is how you can put a digital lock on your shared files:

  1. Set Expiry: Tell Google to stop sharing the file on a specific date.

  2. Disable Downloads: Stop viewers from saving or printing your private work.

  3. Prevent Copying: Turn off the option for others to make a copy of the file.

  4. View-Only Mode: Ensure clients cannot change your words or data by mistake.

  5. Hide Comments: Keep your internal team notes private from the external client.

  6. Use Watermarks: Add your logo to images so people know who owns the work.

  7. Trust Rankings: High security habits help you keep a top search engine rank.

Furthermore, this improves your search engine performance by showing you are a security pro. It makes your company look very organized and ready for 2026 digital growth. This ensures that your intellectual property stays under your total control. It creates a very fast and clear path for your professional peace of mind.


Managing Shared Drives and Folders Correctly

The third phase involves organizing your files so you do not share too much. Clearly, sharing a whole folder is faster but it can also be very risky. Therefore, you should use “Shared Drives” with strict member roles to stay safe today.

Organizing Your Client Folders for Safety

Firstly, create a unique folder for every different client you have in 2026. This allows you to keep one client’s data far away from another client’s view. Secondly, use the “Contributor” role if they need to add files but not delete them.

Furthermore, use the “Viewer” role for anyone who only needs to read your reports. Also, use transition words in your folder names to keep them very easy to find. Lastly, remember that a neat file structure helps your search engine authority and trust. Truly, a clean folder plan is the best tool for avoiding sharing mistakes. It allows you to invite people to work without fearing they will see the wrong file. This is why top agencies use “Client Portals” to manage their work right now.


Monitoring Your Sharing Audit Logs

The fourth phase is where you check who is actually looking at your data. Clearly, you must know if your files are truly staying within your safe circle. Therefore, you must track the “Sharing Activity” in your Google Workspace reports today.

Metrics for a Secure Shared Drive

Firstly, track the “External Sharing” report to see every file shared outside your firm. This helps you see if a team member is sharing too many public links in 2026. Secondly, check the “Audit Log” to see if any unknown devices tried to access your work.

Furthermore, look for any “Large Downloads” that might show a data theft in progress. Also, use your data to see if a secure office leads to more “Client Referrals” for you. Lastly, check your search engine ranking to see if site safety helps your web traffic. Truly, a safe office is a journey that leads to a much stronger brand. It turns a boring task into a series of smart, secure wins for your whole team. This ensures your business stays strong while others face digital leaks.


Keeping Your Drive Safe and Fast

Finalizing your plan requires you to make “Safe Sharing” a part of your office culture. It needs you to train your team and update your sharing rules every single year. Clearly, staying safe in the cloud is a team effort in 2026. Therefore, follow these simple tips to keep your workspace safe and very fast.

Simple Tips for Lifelong File Safety

Firstly, run a “Sharing Audit” once every three months to find any open links. This helps you stay one step ahead of any old project files that are still live today. Secondly, encourage your team to use “Temporary Access” for all short-term contractors.

Furthermore, use transition words in your security emails to keep them very clear and helpful. Also, remind everyone that their clean work helps the company earn more search engine trust. Lastly, check your search engine data to see if safety helps your web traffic grow. Truly, a safe path is a journey that leads to a much better brand in 2026. It builds a path of trust that lets your whole team grow very fast. This secures your future in the digital world for a long time.


Frequently Asked Questions (FAQs)

Q1: Can people without a Google account see my shared files?

Yes, you can use “Visitor Sharing” to let them view files with a secure pin code.

Q2: What happens when an expiry date is reached?

The client loses all access to the file automatically, and they can no longer open the link.

Q3: Does secure sharing affect my website’s SEO?

Yes, brands that handle data safely earn more trust, which is a key signal for search engines.

Q4: How do I stop a client from sharing my file with someone else?

Go to sharing settings and uncheck the box that allows viewers to share the file.

Q5: Is it safer to share a folder or a single file?

Sharing a single file is always safer because it limits what the client can see in your drive.

Also Read: Why your secure your workspace needs an update now